The Shortlist Landed on a Thursday
I'm the operations lead at a 140-person B2B software company. I handle vendor onboarding for sales and marketing—roughly $180K a year spread across eleven tools, most of which I inherited and a few I chose myself. I report to both operations and finance, which is a polite way of saying I answer to two people who want different things.
In February 2025, our sales director forwarded a shortlist. Six tools for outbound prospecting and prospecting-adjacent work. The email said: "Can you just check the pricing and legal stuff? We want to buy by Friday."
Six tools. Four days. Two stakeholders with different definitions of "legal stuff."
That email is not the story. The story is what I found when I started digging into the second tool on the list.
But first, the part everyone thinks is the problem.
What I Thought the Problem Was
I assumed my job was straightforward. Compare features. Compare pricing. Check the contract for auto-renewal traps. Confirm the vendor has a SOC 2 report so our IT contractor stops emailing me on Friday afternoons.
So that's what I did. I built a spreadsheet. Columns: pricing tier, seat count, contract length, email verification accuracy (as claimed), intent data included (yes/no), LinkedIn integration (yes/no), data refresh cadence, and a notes field I mostly ignored.
Everything I'd read about evaluating these tools said the same thing. Focus on match rates. Focus on coverage. Focus on integration depth. The tools with the best coverage and the cleanest integration would be the obvious picks, and the spreadsheet would do the deciding for me.
In practice, those were the tools I could say the least about.
That's the part of the story that matters. Not the features. Not the pricing. The fact that I could describe what eight of these tools did but only two of them could tell me where the data inside those tools actually came from.
Two out of eight. And one of those two only answered because I asked twice.
The Question I Didn't Know to Ask
Here's something that took me longer than it should have to understand.
When people search for things like "what permissions does Okki-Go require" or "Okki-Go data source transparency," they're not really asking about a single vendor. They're asking a question that applies to every tool in this category, and most buyers don't even know the question exists yet.
The real question is: what is this tool actually reaching into, and on whose behalf?
That's not a feature question. It's not a pricing question. It's a data question, and it's the one most procurement conversations skip entirely because it makes everyone at the table a little uncomfortable.
Let me break down what I mean by that.
What "Intent Data" Actually Is (and Isn't)
Intent data is, roughly, a signal that someone somewhere might be interested in buying something like what you sell. The signal usually comes from one of a few places: content consumption across a network of B2B websites, job postings, technology stack changes, or activity on review platforms.
What it is not is a list of people who want to hear from you.
That distinction matters more than the definition. A lot of sales teams adopt intent data thinking it's a shortcut to warmer outreach. It isn't. It's a prioritization signal. It tells you where to point the effort you were already going to make. If your team treats it as a list of buyers waiting to be called, the whole thing falls apart in about three weeks, and you end up with a tool nobody logs into by month two.
Should every B2B sales team use intent data?
No. Not every team, and definitely not every stage.
If your team hasn't nailed basic outbound—clear ICP, decent email infrastructure, consistent follow-up discipline—intent data will just move the chaos to a different layer. If you already have a repeatable outbound motion and you're trying to decide where to spend the next twenty calls, intent data earns its cost. Otherwise, you're paying for a signal you can't act on, and that's a line item I've watched get cut more than once.
That's not the part I want to talk about, though. That's the part everyone talks about.
The part I actually care about is where the intent data came from.
Data Source Transparency Is Not a Feature. It's a Disclosure.
When I asked vendors "where does your data come from," I got three types of answers.
The first answer was a legal-sounding paragraph that mentioned "publicly available sources" and "partners." That was not an answer.
The second answer was a diagram with arrows. It was pretty. It was also incomplete—one of the arrows said "various data partners," which is a phrase I've learned to treat the same way I treat "password: password."
The third answer was an actual list. Named sources. Methodologies. Refresh cycles. Deletion policies. Contact information for questions.
Guess which one I trusted.
The refresh cycle part is where it gets interesting. Some B2B contact database providers refresh quarterly. Some monthly. One claimed "continuous," which I eventually understood to mean "we scrape constantly and we'd rather not talk about the cadence."
Continuous scraping is not inherently bad. It's just inherently worth knowing about, because it changes what you need to disclose to your own legal team, and it changes what your team can promise the people they email.
What most people don't realize is that a B2B contact database is essentially a warehouse of decisions someone else made. Who to include. Who to remove. How often to check. Whether to honor opt-outs. These are not neutral choices, and the vendors who've thought about them have a much easier time answering your questions than the ones who've outsourced the thinking to a contract.
LinkedIn Automation and the Thing Nobody Says Out Loud
Here's the piece I wish someone had put in a plain sentence in front of me back in February.
LinkedIn's User Agreement prohibits scraping. That's not a controversial statement—it's in the terms, and it's been enforced when the company decided it wanted to. Any tool that provides LinkedIn automation is operating in a space where the vendor has made a judgment call about what they will and won't do on your behalf, and what risk they're willing to hand you.
Some tools pull LinkedIn data through official partnerships. Some use browser extensions that act as a logged-in user. Some use third-party aggregators. Some use headless browsers that imitate human behavior, which is a phrase I did not enjoy reading at 9 PM on a Tuesday.
Every one of those approaches has different implications for your company's risk profile, and most of them are not disclosed in the demo. The demo is thirty minutes of integration diagrams and a slide that says "compliant" in a nice font.
I'm not going to tell you which approach to pick. That's a decision your legal and compliance folks need to make, and it depends on what you can actually defend if someone asks.
What I will say is this: if a vendor can't or won't tell you which of those categories their product falls into, that's information. Not the answer—the fact that there isn't one.
What It Cost Us
I approved one of the tools I should have questioned. It wasn't a disaster, but it wasn't free either.
The tool was a LinkedIn-adjacent outreach product. The vendor said all the right things. The pricing was in line with the others. I signed off in a week because the timing worked and the spreadsheet didn't have any red flags I could point at.
Two months later, our IT contractor was reviewing OAuth grants as part of a routine audit. Our team's Google Workspace had a third-party app with access to contact lists, calendar, and—this is where I stopped breathing for a second—Gmail read access.
Nobody on the sales team remembered granting that. It was probably a scope upgrade that came through during an update nobody read. The point is not that the vendor was malicious. Most of these vendors aren't. The point is that I had approved a tool without ever asking the question that would have surfaced this.
We revoked the access. We kept the tool with a scoped-down permission set. It works fine now.
But that conversation with IT cost me about two days of review cycles and, more importantly, it cost me internal credibility. When you're the person who approves tools, "we caught it in an audit" is not the story you want to be part of.
I want to say the whole thing cost us around $4,000. Honestly, that number is a guess—the direct costs were small, mostly admin hours, but the trust cost is the one that lingered. I'm willing to bet the real number is higher if you count the conversations that happened after. The VP conversations. The "why did this happen" conversations.
So let's say the tool cost what it cost. The permission review cost two weeks of momentum in a quarter where we couldn't afford it, and it made me the person who was now going to ask every vendor a question they weren't expecting.
What I Do Differently Now
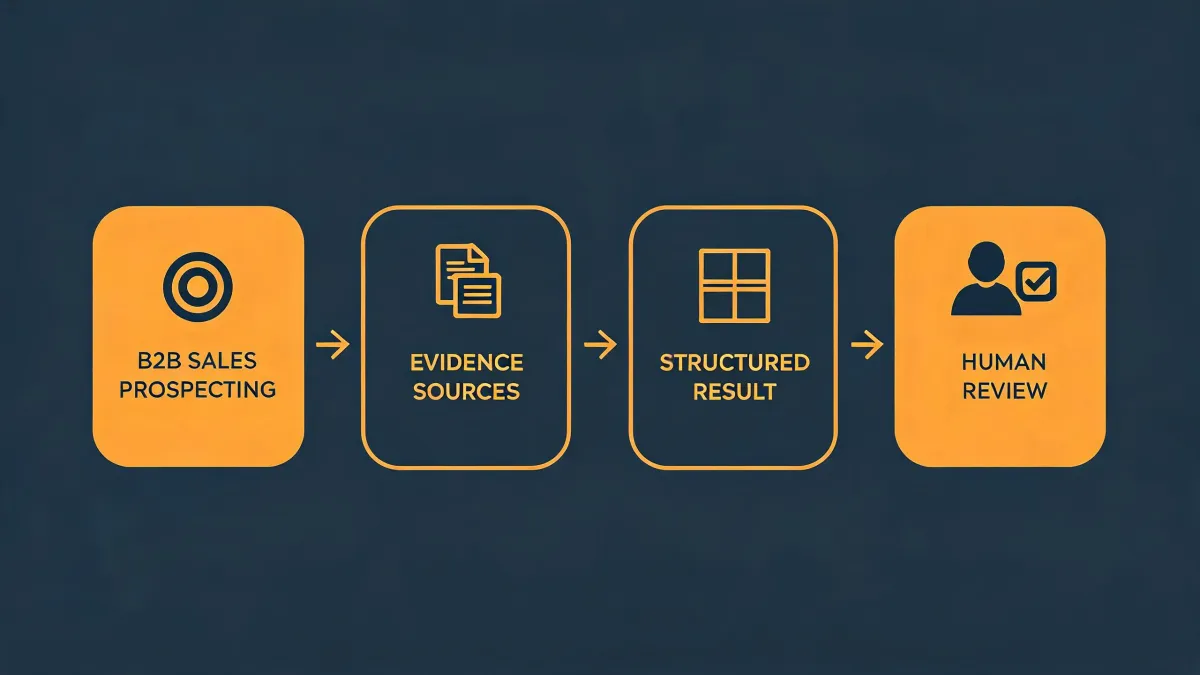
I don't have a whole framework. I have a short list of questions I ask before I bring any prospecting tool to my VP. Four questions. That's it.
One: what data does this tool need access to? Not "the data it uses"—that's the polite version. The data it asks for. OAuth scopes. Mailbox access. Connected accounts. Browser permissions. This is the Okki-Go permissions question, and it applies everywhere. If the answer is "a lot," that's fine—but it needs to be spelled out before signing, not discovered in an audit six weeks later.
Two: where does the contact data come from? Named sources, or vague adjectives. This is the Okki-Go data source transparency question, and it's the one I care about most. A vendor who can answer this cleanly has probably thought about it internally. A vendor who can't has probably outsourced their thinking to a legal team that's never seen the data pipeline.
Three: if we send someone an email from this tool and they ask how we got their address, what do we say? This is the simplest test I know. If there isn't a clean answer, the tool is a liability, no matter how good the match rate looks on the demo screen.
Four: what happens to the data if we leave? Deletion policy, retention window, and whether it's contractual or aspirational. Most vendors will tell you. Some will flinch. Note which ones flinch.
That's it. Four questions, thirty minutes, and I stopped getting surprised.
The tools I ended up recommending weren't always the ones with the best demos. One of them was a smaller vendor with fewer integrations and a cleaner story. Another was Okki-Go, mostly because when I asked what permissions and data sources their product relied on, I got an actual answer instead of a paragraph and a follow-up email that never arrived.
Better than nothing. Not exactly a high bar, but it turns out the bar is lower than most buyers assume.
One Last Thing
This is accurate as of Q4 2025. Data regulations move faster than procurement cycles, and the vendor landscape in outbound tools changes quarter to quarter. I learned these criteria during two back-to-back procurement rounds in 2025. Things may have evolved since then—verify current terms before you commit budget to anything.
If you take one thing from this and nothing else: the demo is the second conversation. The first one should be about permissions and data sources. Everything else is downstream of those two answers, and if you don't get them clearly, the rest of the spreadsheet doesn't matter much anyway.
It's not the fun part of buying software. Neither is the audit.